blueNull
Audits realized A/B counts for achieved minimum detectable effect and integrity issues (sample-ratio mismatch, exposure dilution), and signs the result — so a “not significant” dashboard reading can be checked against whether the test could have detected anything at all.
Experimentation and analytics reviewers.
Not a causal-inference platform. A NULL_LICENSED verdict does not claim the underlying effect is exactly zero. It audits the counts it is given; it does not run the experiment, pull data from an experimentation platform, or evaluate interference between arms (marked NEVER-EVALUATED on every V1 certificate).
blueNull is for the moment a dashboard says "not significant" and someone asks whether the test could have seen anything at all. It audits the realized counts of an A/B test for achieved minimum detectable effect and for integrity problems such as a sample-ratio mismatch, and signs what it found. The three screens below follow one declared audit: the history where every run is sealed and timestamped, the certificate for a run that failed its own integrity check, and the verifier that checks a certificate without the server that produced it.
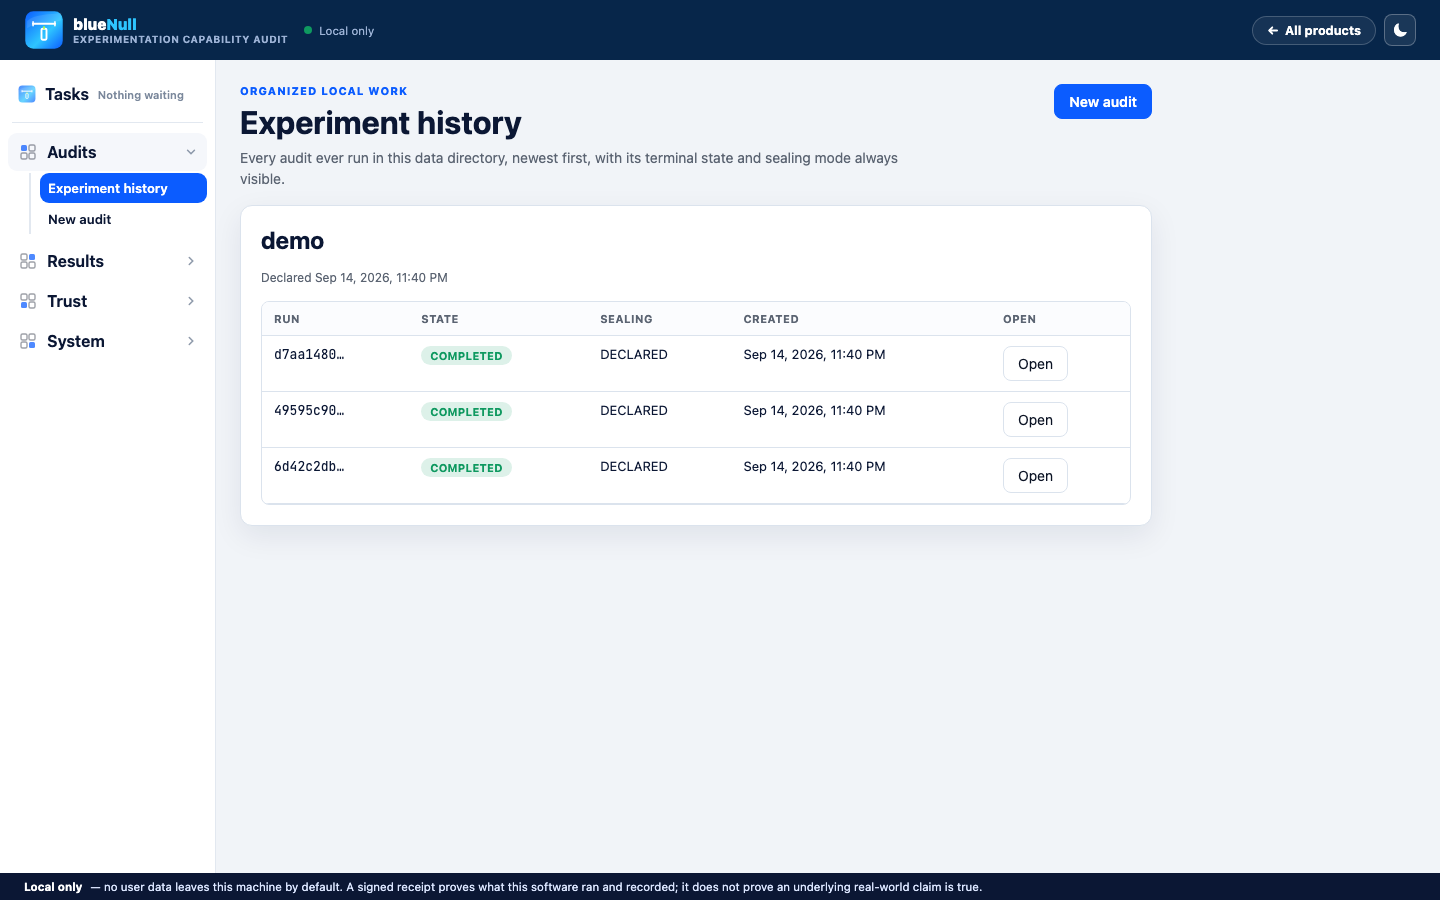
Experiment history — every audit ever run in this data directory, newest first, with its terminal state and sealing mode always visible. Sealing DECLARED means the audit's contract — the effect size the test had to be able to detect — was registered before the data was first seen; an audit declared after the fact is sealed POST-HOC and says so.
Open a run and the certificate shows what was measured.

Run detail — this run is Broken before lift is even discussed: the realized 6,000/4,000 split fails its own sample-ratio check at p=5.5e-89 against a declared 50/50 allocation, so the observed +0.00pp lift is not trustworthy evidence of anything. Of the four integrity checks, one failed, one passed, and two are marked NEVER-EVALUATED rather than silently skipped.
The signed certificate for this run verifies independently of the dashboard that produced it.
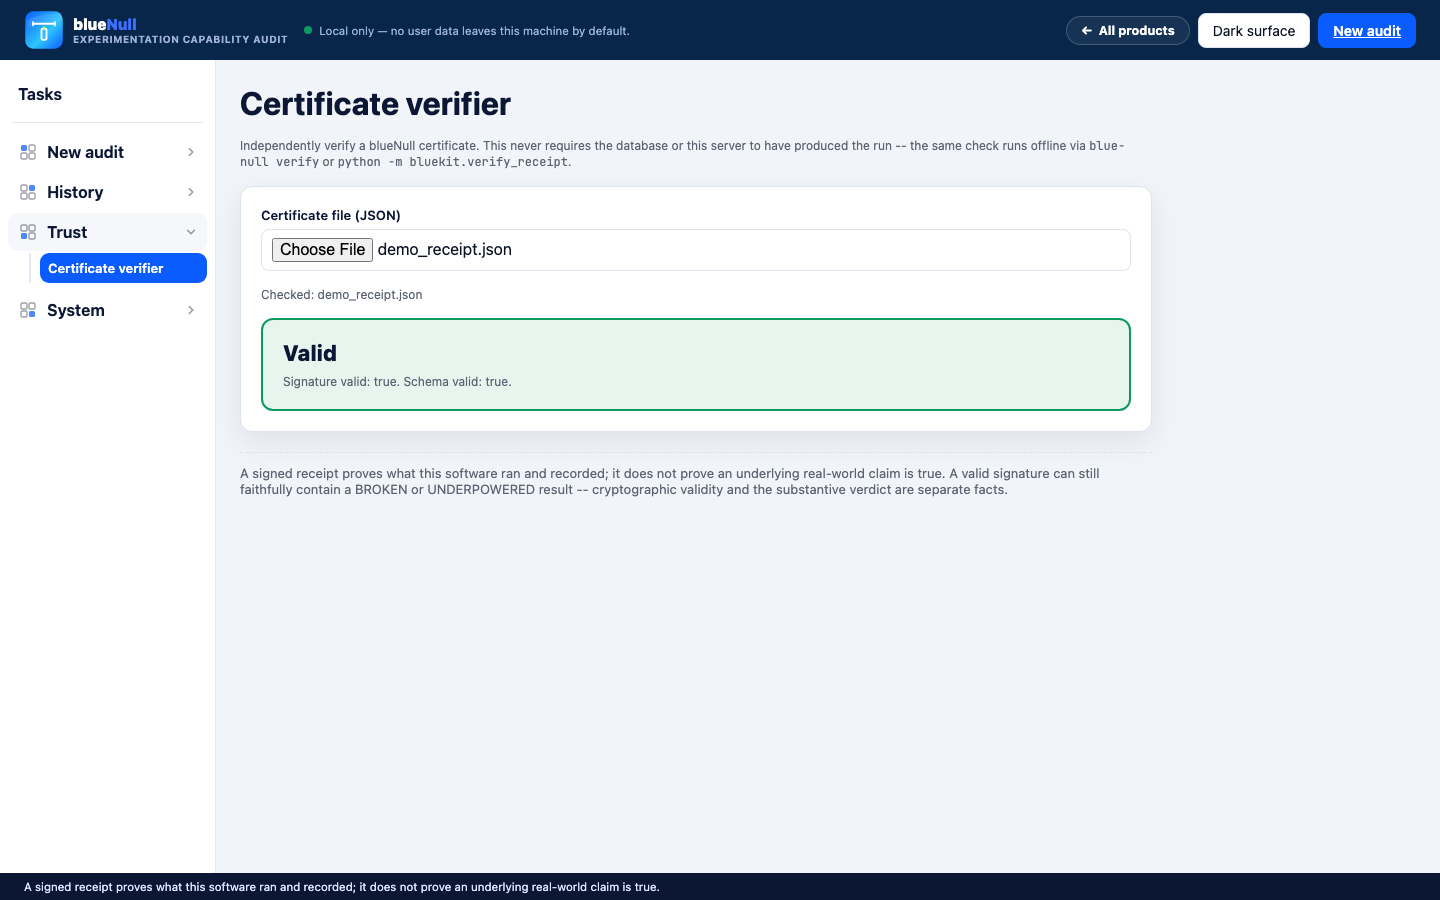
Certificate verifier — Valid means the signature and schema check out: this is the certificate blueNull issued, unaltered. It says nothing about the verdict inside, which can be BROKEN or UNDERPOWERED and still verify; the screen calls those two separate facts. The same check runs offline from the command line, without this server or its database.
Backend, CLI, API, and web dashboard exist with a seeded end-to-end demo. See the status page for exactly what's built.